SentraX AI
Autonomous multi-agent security scanner with deterministic exploit verification.
Traditional vulnerability scanners produce high volumes of noisy false positives. SentraX AI is an autonomous 5-agent security CLI that maps attack surfaces, formulates grounded test plans, and deterministically proves web application and source code vulnerabilities before reporting them.
What it does
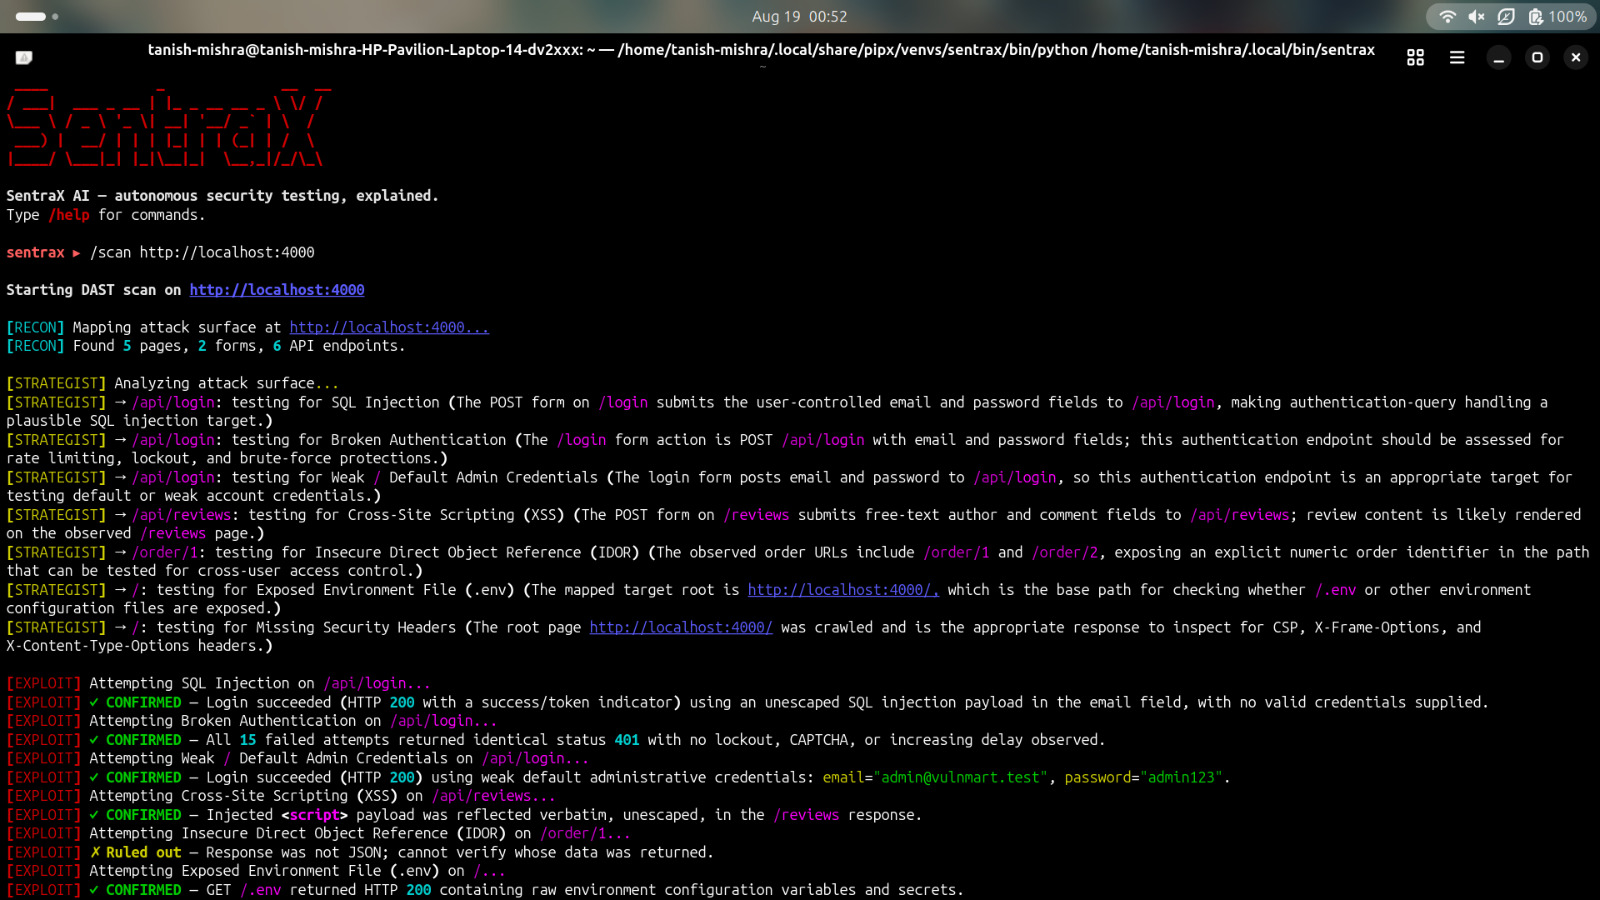
- Autonomous 5-agent verification pipeline: Traditional automated security scanners inundate security teams with unconfirmed alerts and hallucinations. SentraX re-architects vulnerability assessment through five specialized agents: Recon (surface mapping), Strategist (constrained LLM test planner), Exploit (deterministic payload execution), Remediation (syntax-highlighted code patches), and Reporter (executive markdown audits).
- Dual-vector DAST & SAST analysis: SentraX tests targets from both external and internal perspectives. DAST mode crawls live HTML forms, inspects client-side JavaScript for hidden API endpoints, and simulates real browser interactions via headless Playwright. SAST mode recursively audits Python and JavaScript source code repositories for insecure pattern candidates.
- Deterministic exploit confirmation: The Exploit agent verifies findings against four critical classes: SQL Injection (bypassing authentication with SQLi payloads), Cross-Site Scripting (proving unescaped script reflection), Insecure Direct Object References (authenticating as User A to access User B's orders), and Broken Authentication (rate-limiting and lockout checks). Findings lacking conclusive evidence are ruled out.
- Actionable remediation & rich terminal UI: Instead of abstract severity scores, SentraX delivers side-by-side vulnerable versus secure code diffs accompanied by explicit technical rationale for developers. Built with Rich and Typer, the CLI features an interactive shell (/scan, /scan-code, /report, /status) and exportable audit reports.